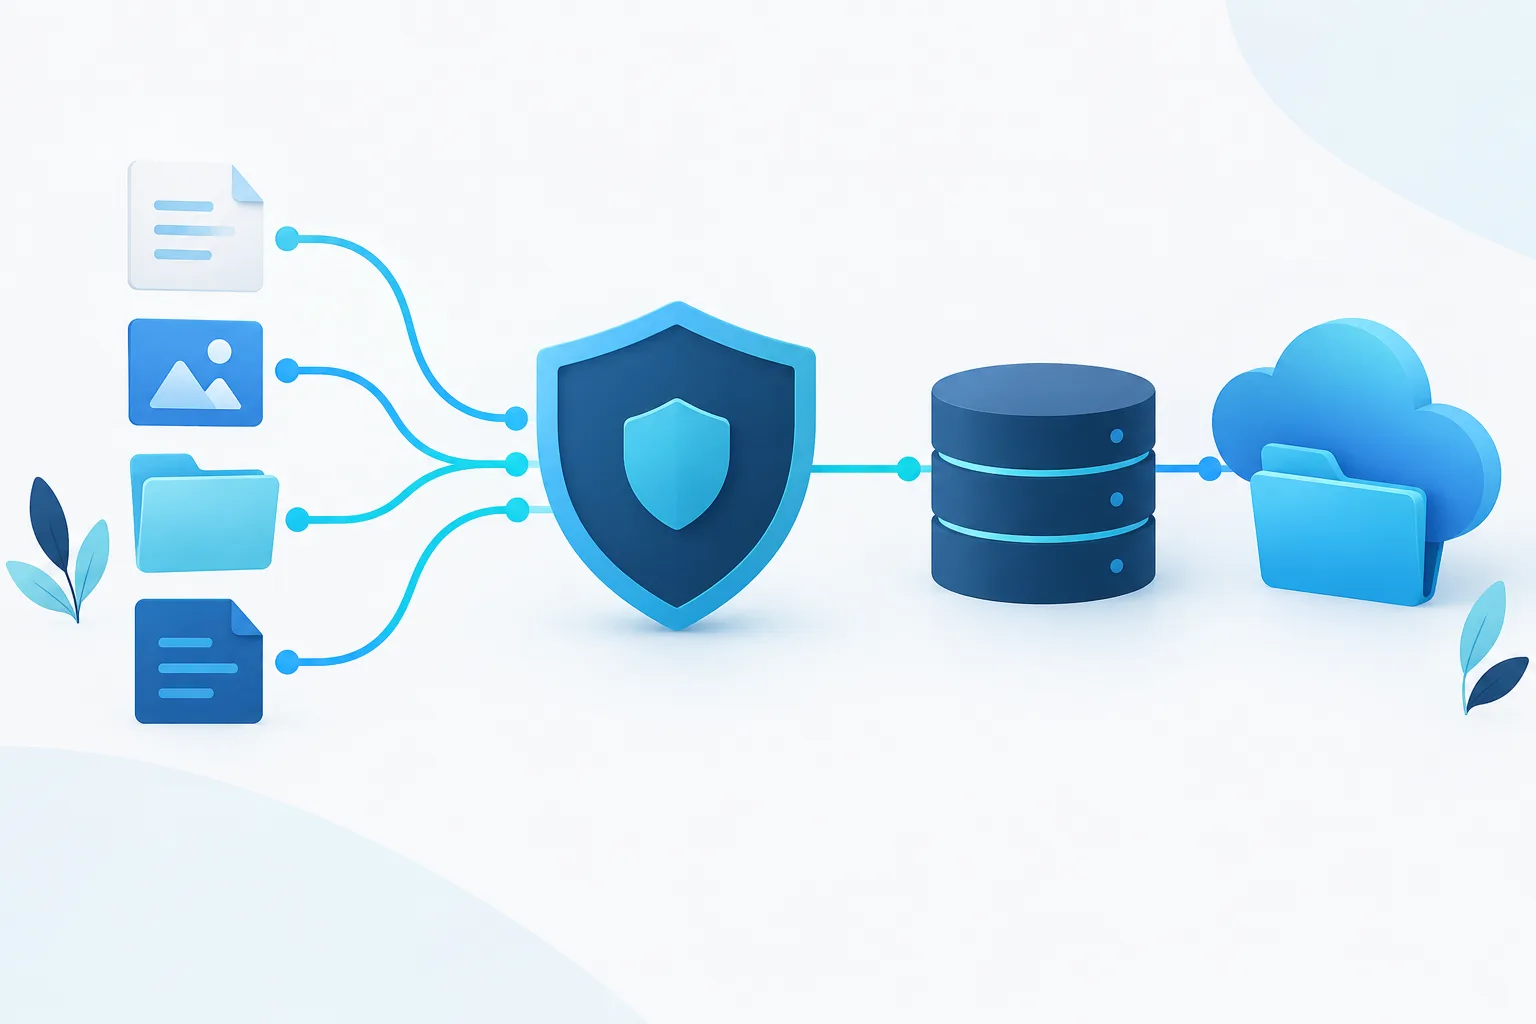
WordPress law firm intake form security involves more than choosing a form plugin or adding an SSL certificate. A submission may pass through the WordPress dashboard, a plugin, email, backups, or connected services. Before launch, a firm should understand each stop and who can access the information there.
The goal is to assess the whole path from submission to deletion, not just the form itself. Use this checklist to guide a practical review with the people responsible for the website, the form, and the firm’s intake process.
Map a test submission from start to finish
Start with a test entry using dummy information. Follow it through every system that receives, stores, copies, or processes it. Ask the person who manages the website or plugin to demonstrate the path rather than relying only on assumptions about how the form works.
Check whether the submission appears in the WordPress dashboard or plugin interface, and whether the plugin saves entries to the WordPress database. Find out if uploaded files are stored separately, where they are kept, and whether the form creates records in logs. Then trace any copies sent to backups, an email provider, a customer relationship management system, or an automation service.
Do not assume that a form behaves like another plugin you have used. Storage and export options can vary. Confirm the specific plugin’s practices and settings, and document the answers in a simple data-flow record. For broader website upkeep considerations, see these WordPress site management practices.
Review access in WordPress and the form plugin
WordPress user roles are only one part of the access picture. Review who can sign in to the site, then check whether the form plugin has separate permissions for viewing, exporting, deleting, or forwarding entries.
- List people and accounts: Identify staff, web administrators, contractors, and other vendors with access to WordPress, the plugin, hosting, backups, or related email accounts.
- Check what each account can do: Confirm which users can see submissions and which can download, export, change, or delete them. Do not treat permission to edit a page as automatically equivalent to permission to read intake records.
- Review shared or older accounts: Look for accounts that are no longer needed, are shared among multiple people, or have broader access than their work requires. Decide who is responsible for removing access when responsibilities change.
- Check vendor access: Ask whether hosting, maintenance, support, or email providers can access stored submissions while providing their services. Understand how that access is controlled and how support requests are handled.
Keep the access review specific to intake data. A person may not need to view submissions to update the site, and a vendor may not need ongoing access simply because it was once useful for setup. Plugin settings and update compatibility can affect how controls behave, so review the plugin’s permissions after configuration changes. This guide to WordPress plugin compatibility offers related maintenance context.
Understand storage, backups, and logs
Ask the plugin or website administrator where entries are stored and how to remove them. If submissions are in the WordPress database, determine who has access to that database through the site or hosting environment. If files can be uploaded, identify their storage location and whether they can be accessed through a public link.
Include backups in the review. A deleted submission may remain in a backup until that backup is replaced or removed, depending on the backup process. Ask how backups are protected, who can restore them, and what happens to form records when a restore is performed. A recovery process should be understood before an incident, not improvised afterward.
Also ask what the site and plugin record in logs. Logs can be useful for administration, but the firm should understand whether they contain form answers, file details, or other sensitive information. Confirm where logs are kept, who can view them, and how long they remain available. Avoid assuming that a record is gone just because it has been removed from the form’s entry list.
Test notifications and every recipient
Email notifications can make intake easier to manage, but they can also create another copy of submitted information outside WordPress. Use dummy data to test the form. Inspect the message itself, including its subject line, body, attachments, and any links to view the entry.
- Check whether the email includes full answers or only a general alert.
- Confirm the recipient list, including any shared inboxes, forwarding rules, or notification services.
- Find out whether uploaded files are attached or linked, and who can access them.
- Ask which email systems retain a copy and who can search or export those messages.
- Check what happens when staff use mobile notifications or another connected service.
Choose notification settings deliberately. If a brief alert is enough to prompt an authorized person to sign in and review an entry, consider whether the email needs to reproduce the visitor’s answers. For more detail on handling form-related email, read how WordPress form notifications can be handled more carefully.
Collect only what is appropriate at the intake stage
Review the form’s questions with the people responsible for intake. Ask what information is needed for an initial response and whether each field serves that purpose. Unnecessary questions can encourage visitors to submit details the firm does not need at this stage.
Make the visitor notice easy to find before submission. It should explain the purpose of the form, how the firm expects to respond, and any limits on using the form to share information. Avoid language that could lead a visitor to believe that submitting a form establishes a relationship or that the form is the right channel for urgent matters, unless the firm has approved that wording for its process.
Make sure the notice reflects what actually happens to the data. If entries go to a third-party service, are emailed, or are retained in backups, the firm should account for those destinations when reviewing its wording. Have the appropriate firm decision-makers review the form’s notice and retention approach; this checklist is not a substitute for that review.
Set a retention and deletion process
There is no single retention period that fits every firm and intake workflow. Establish a policy with the appropriate decision-makers rather than leaving records in the plugin indefinitely by default. The policy should cover submissions that do not proceed, uploaded files, email copies, logs, and backup copies.
Decide who may delete records and how deletion is verified across the systems identified in the data map. If the plugin has an export or delete function, test it with dummy data and document what the function removes and what it does not. Make sure staff know how to handle a request or internal instruction to remove an entry.
Before launch: a practical review
- Submit dummy information and trace it through the database or plugin dashboard, files, logs, backups, email, and connected services.
- Review WordPress accounts and the form plugin’s separate access controls.
- Test notification emails and confirm exactly what is sent and who receives it.
- Review each question and the visitor notice together.
- Agree on retention, deletion, and backup handling with the appropriate firm decision-makers.
- Repeat the review after significant plugin, notification, or workflow changes.
Frequently asked questions
Who can view WordPress intake form submissions?
It depends on the site’s user permissions, the form plugin’s controls, and access to connected systems such as email or hosting. Check each layer rather than relying on WordPress roles alone.
Do WordPress form plugins store submissions in the database?
Storage depends on the plugin and its settings. Confirm whether entries are saved in the WordPress database, elsewhere, or both, and check how file uploads and logs are handled.
Can email notifications include sensitive intake details?
They can, depending on the form’s notification settings. Test with dummy data and inspect the message, attachments, recipients, and any connected email or forwarding services.
How should a firm decide how long to retain submissions?
Set a retention approach with the appropriate firm decision-makers. Account for entries, uploaded files, email copies, logs, and backups, and document how deletion is carried out.
Conclusion
A careful review traces intake information through every system, checks who can reach it, and limits what is collected and copied. If you would like to discuss managed WordPress support for your site, you can learn about Zevonix Cloud’s managed WordPress services.